How Packet Filtering Works
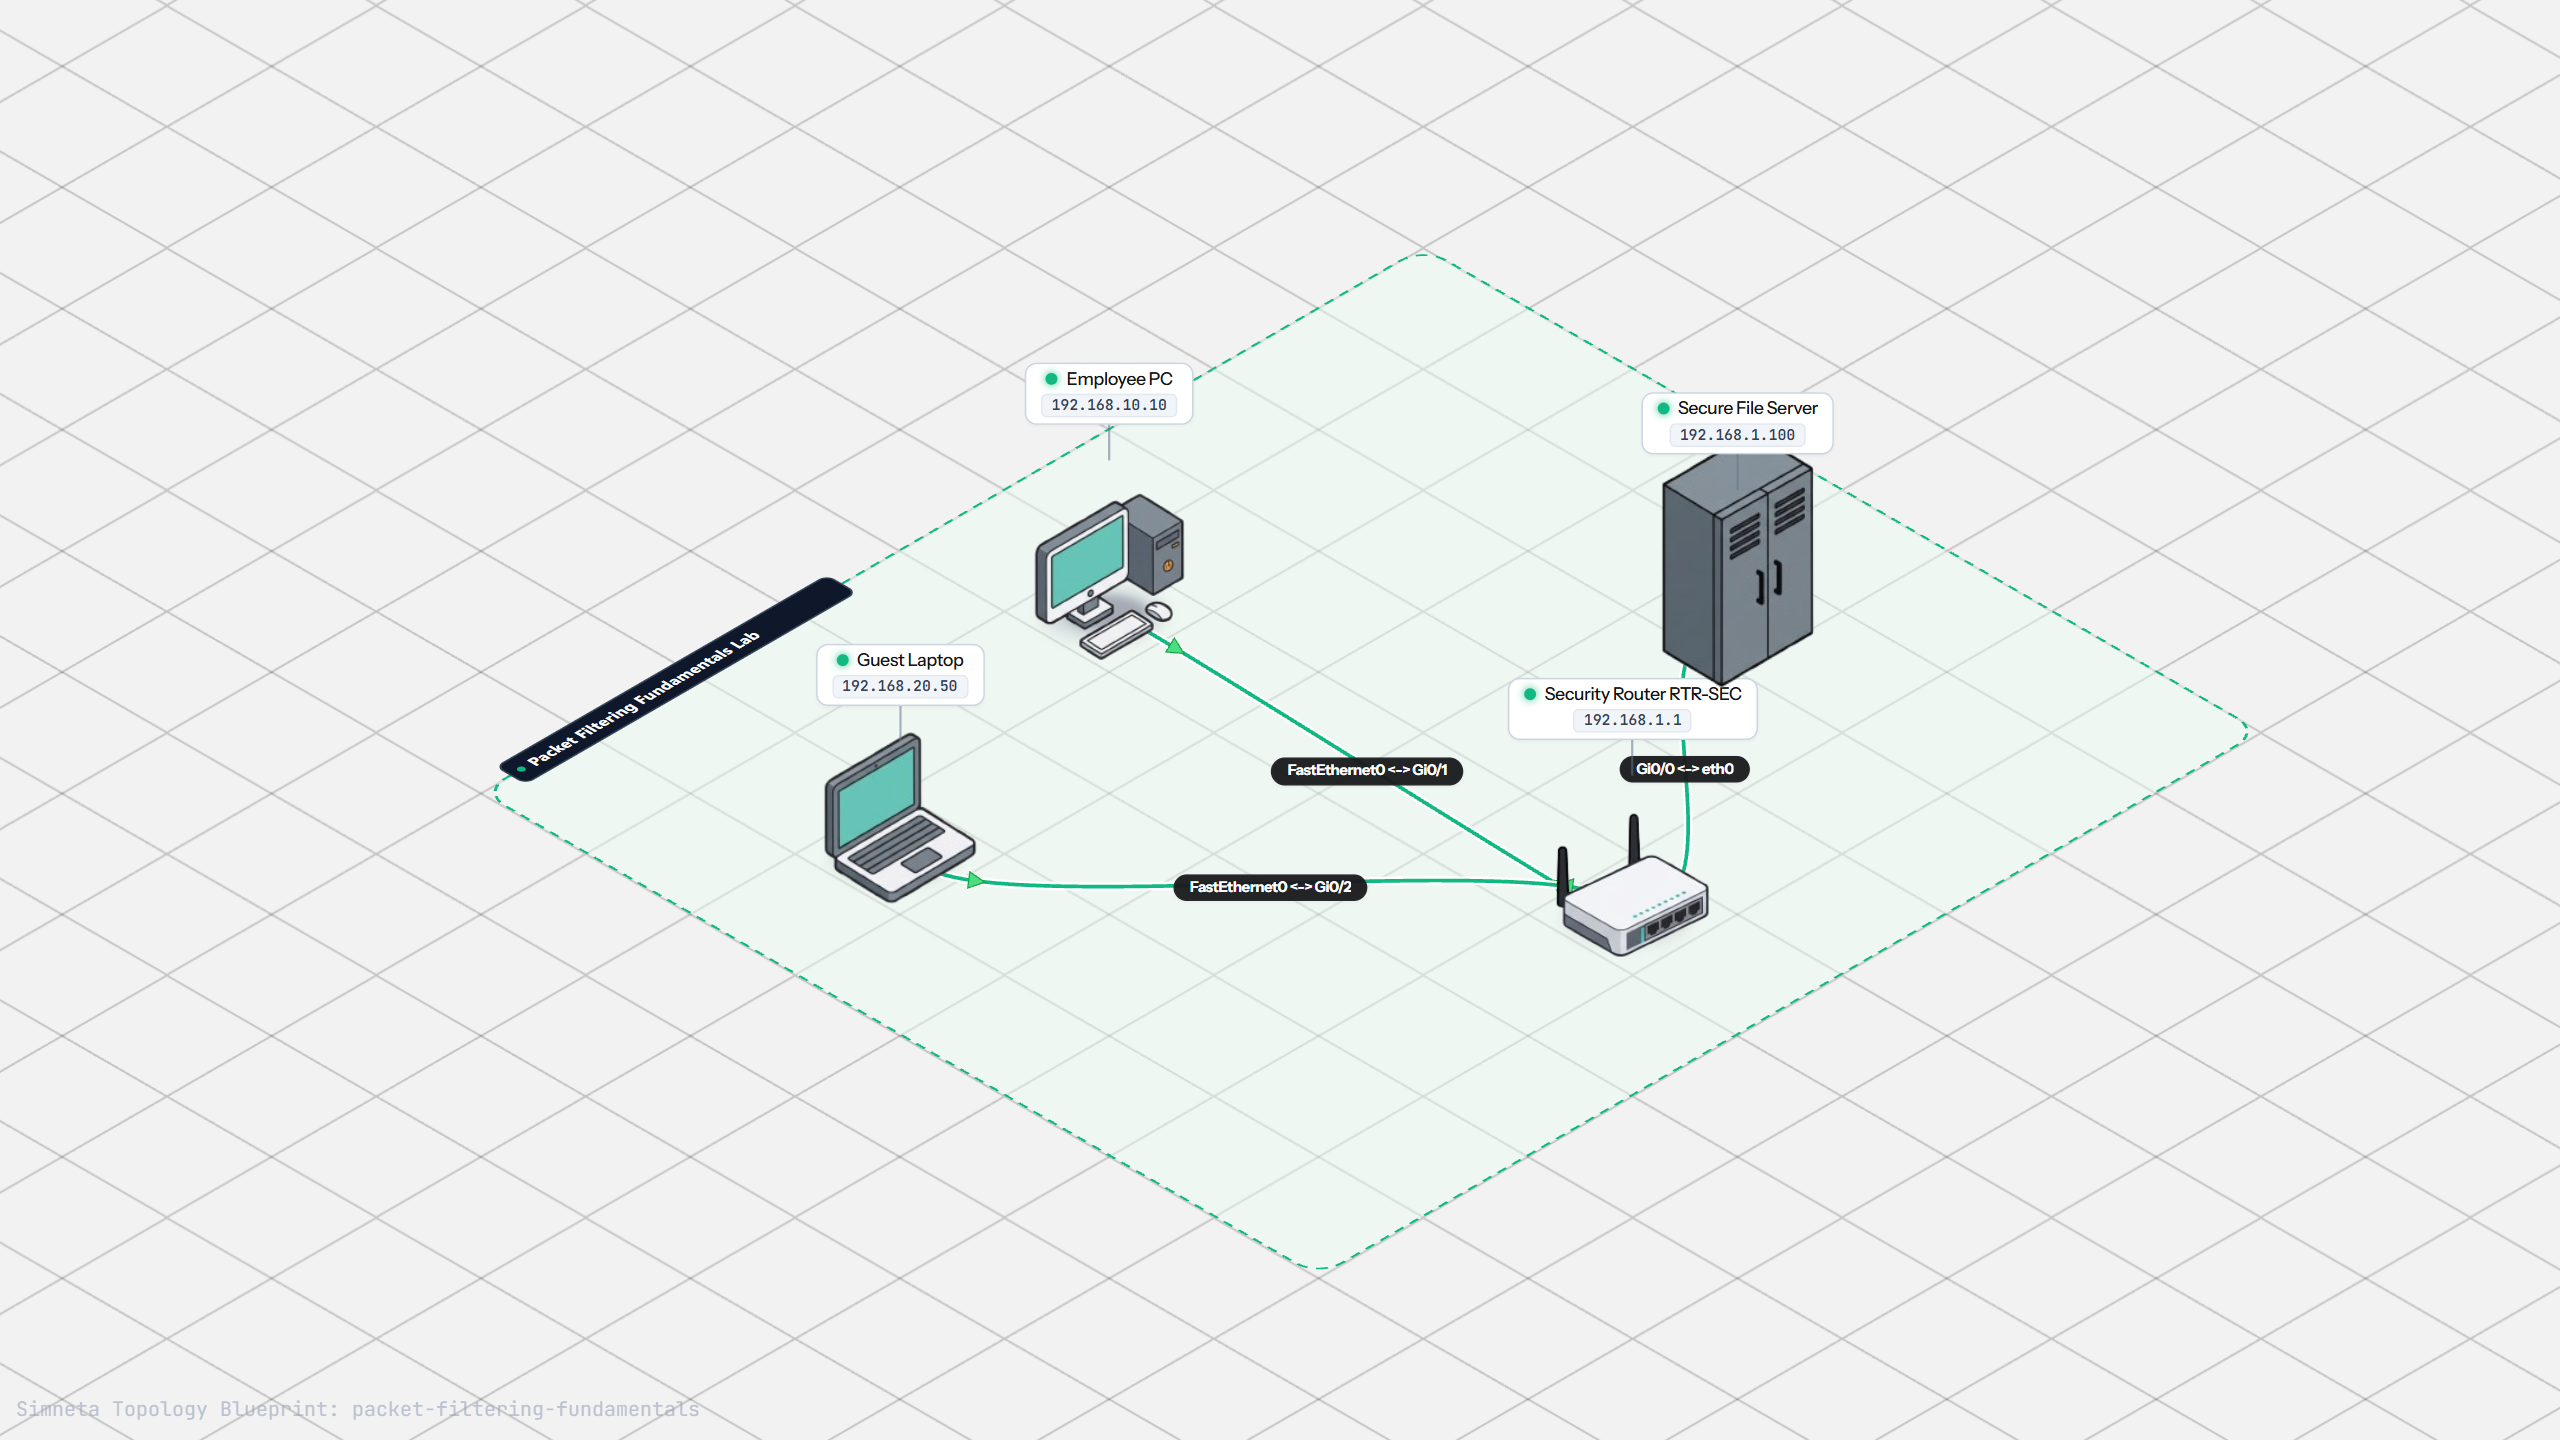
Understand how firewalls and routers inspect packet headers, evaluate access control lists in top-down sequential order, and apply the implicit deny rule.

Master packet filtering fundamentals, standard and extended access control lists, port-based traffic
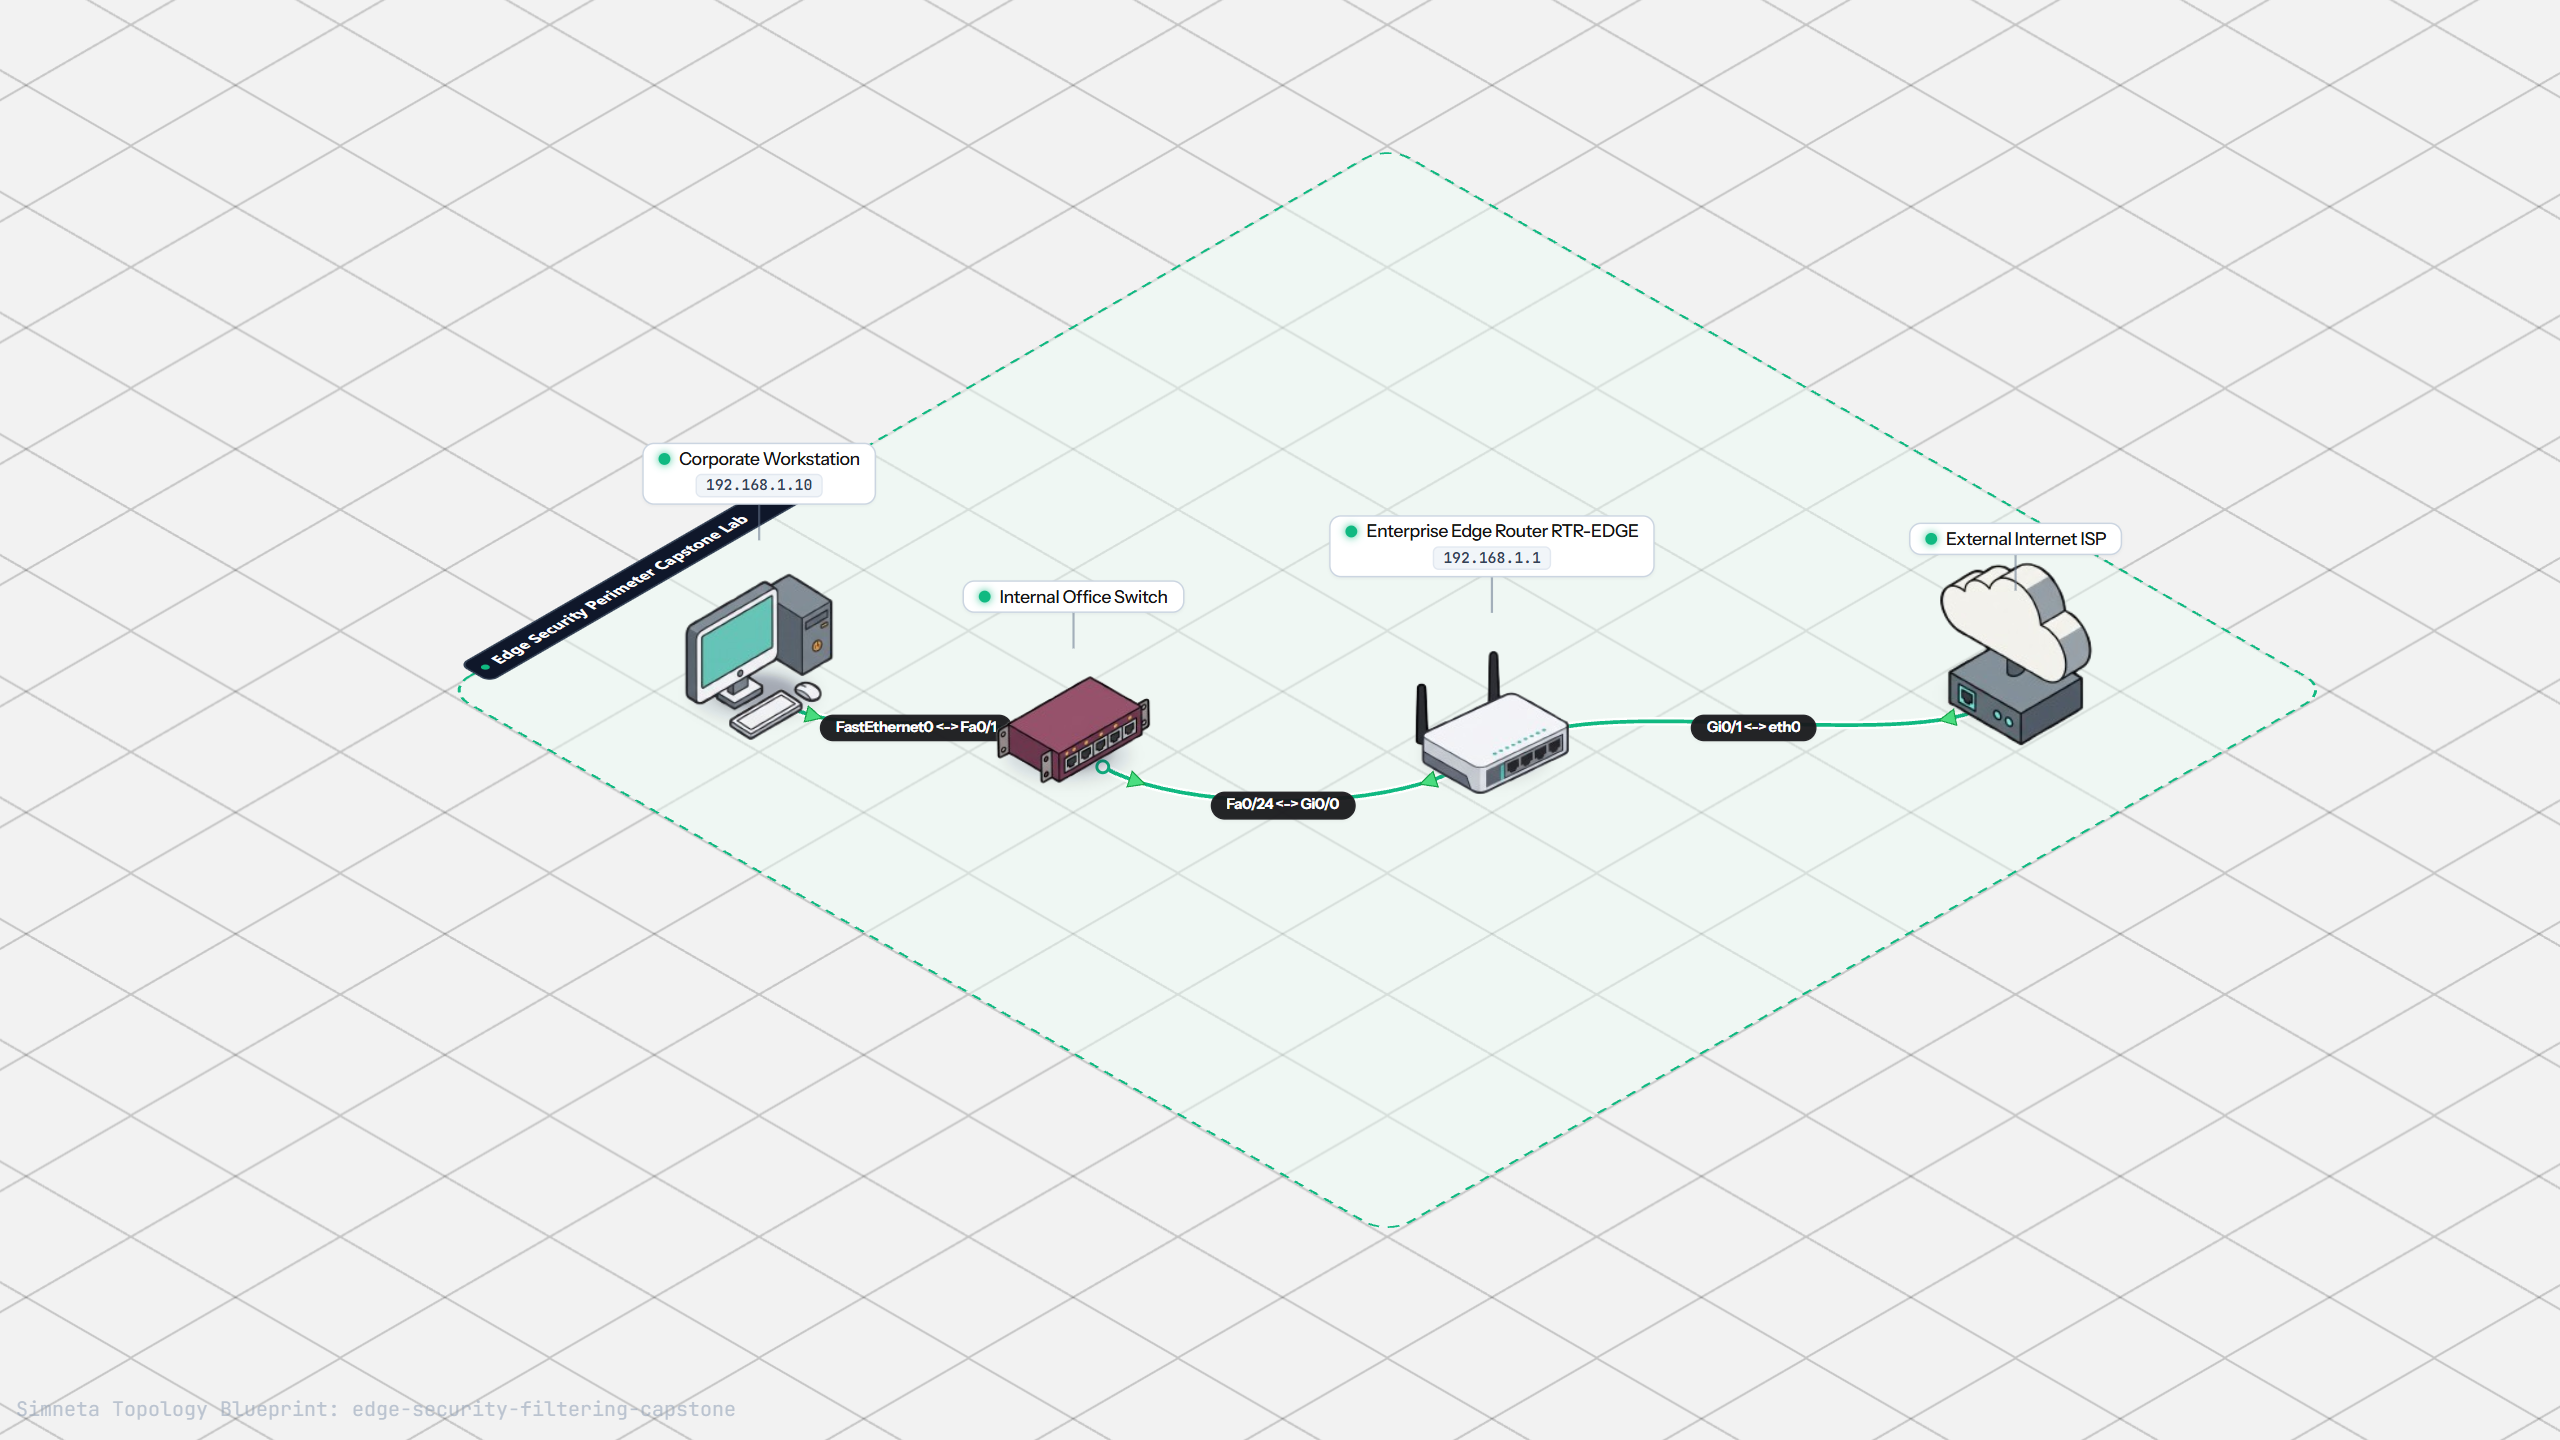
Master packet filtering fundamentals, standard and extended access control lists, port-based traffic restriction, and edge perimeter defense in practical NetLab topologies.
Learn step by step. Each chapter includes practical tasks and an interactive topology.
Understand how firewalls and routers inspect packet headers, evaluate access control lists in top-down sequential order, and apply the implicit deny rule.

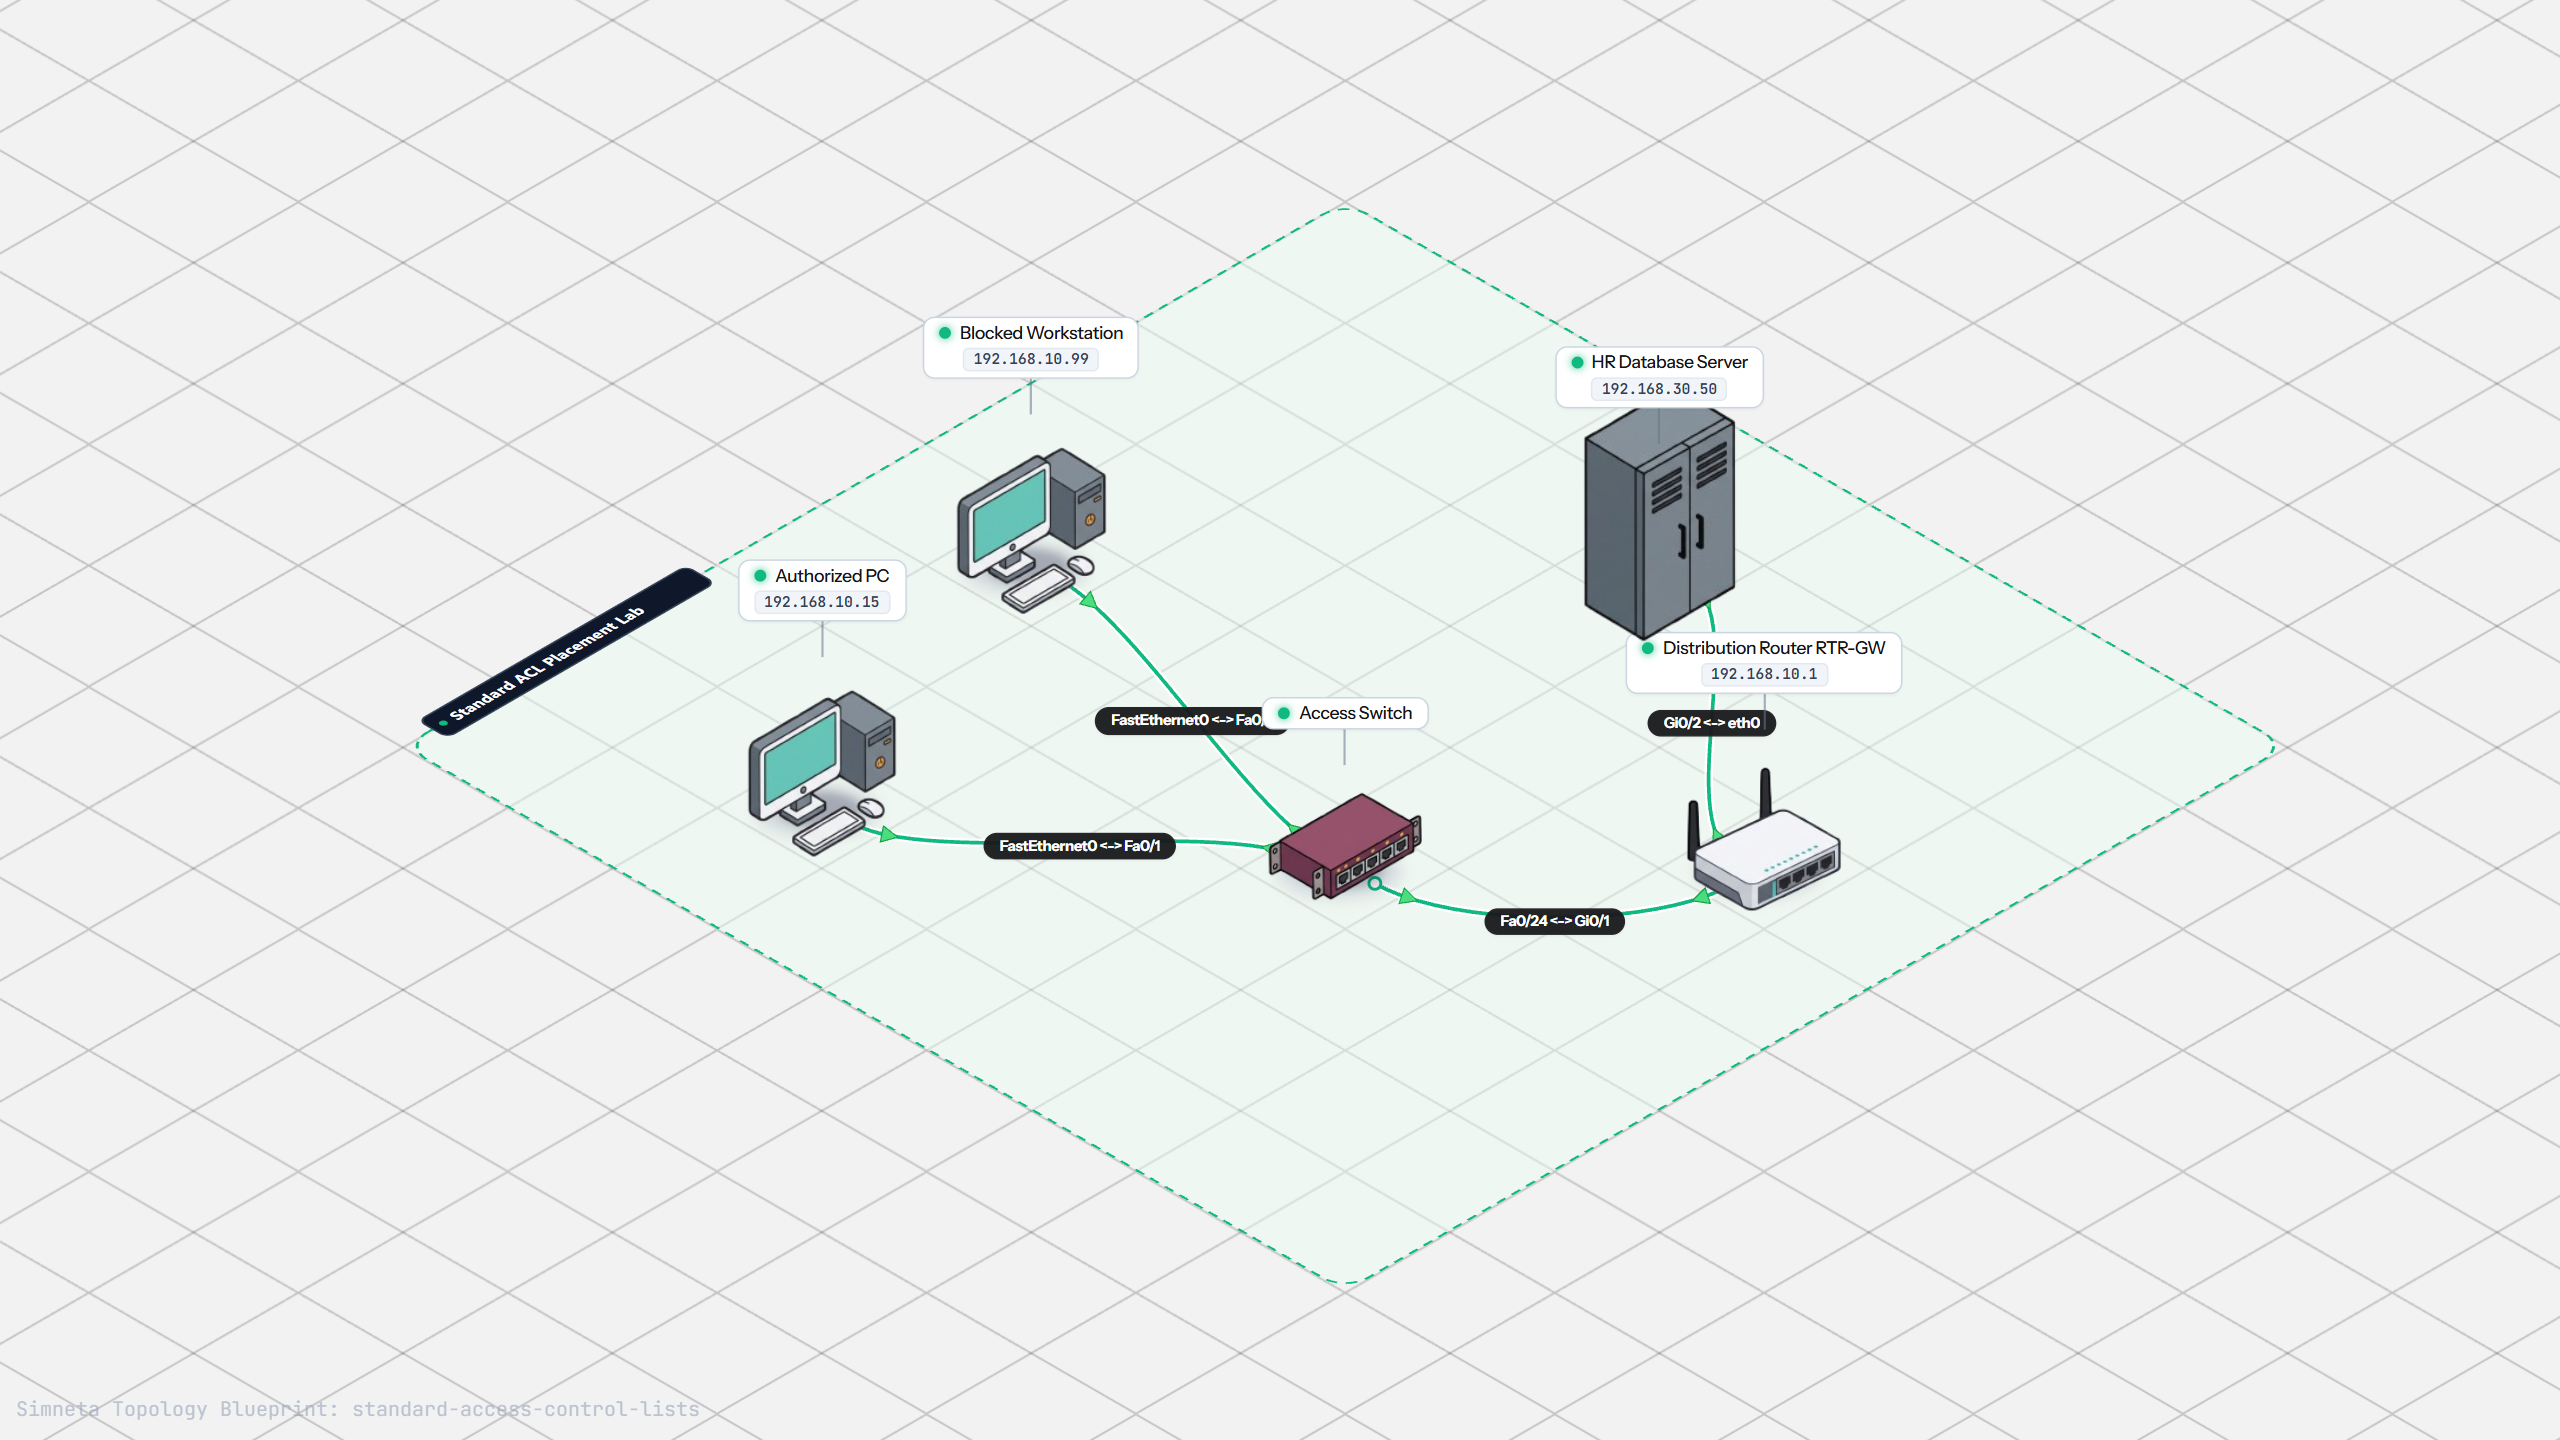
Build numbered and named standard access control lists. Master wildcard mask bit calculations and learn why standard ACLs must be placed close to the destination.

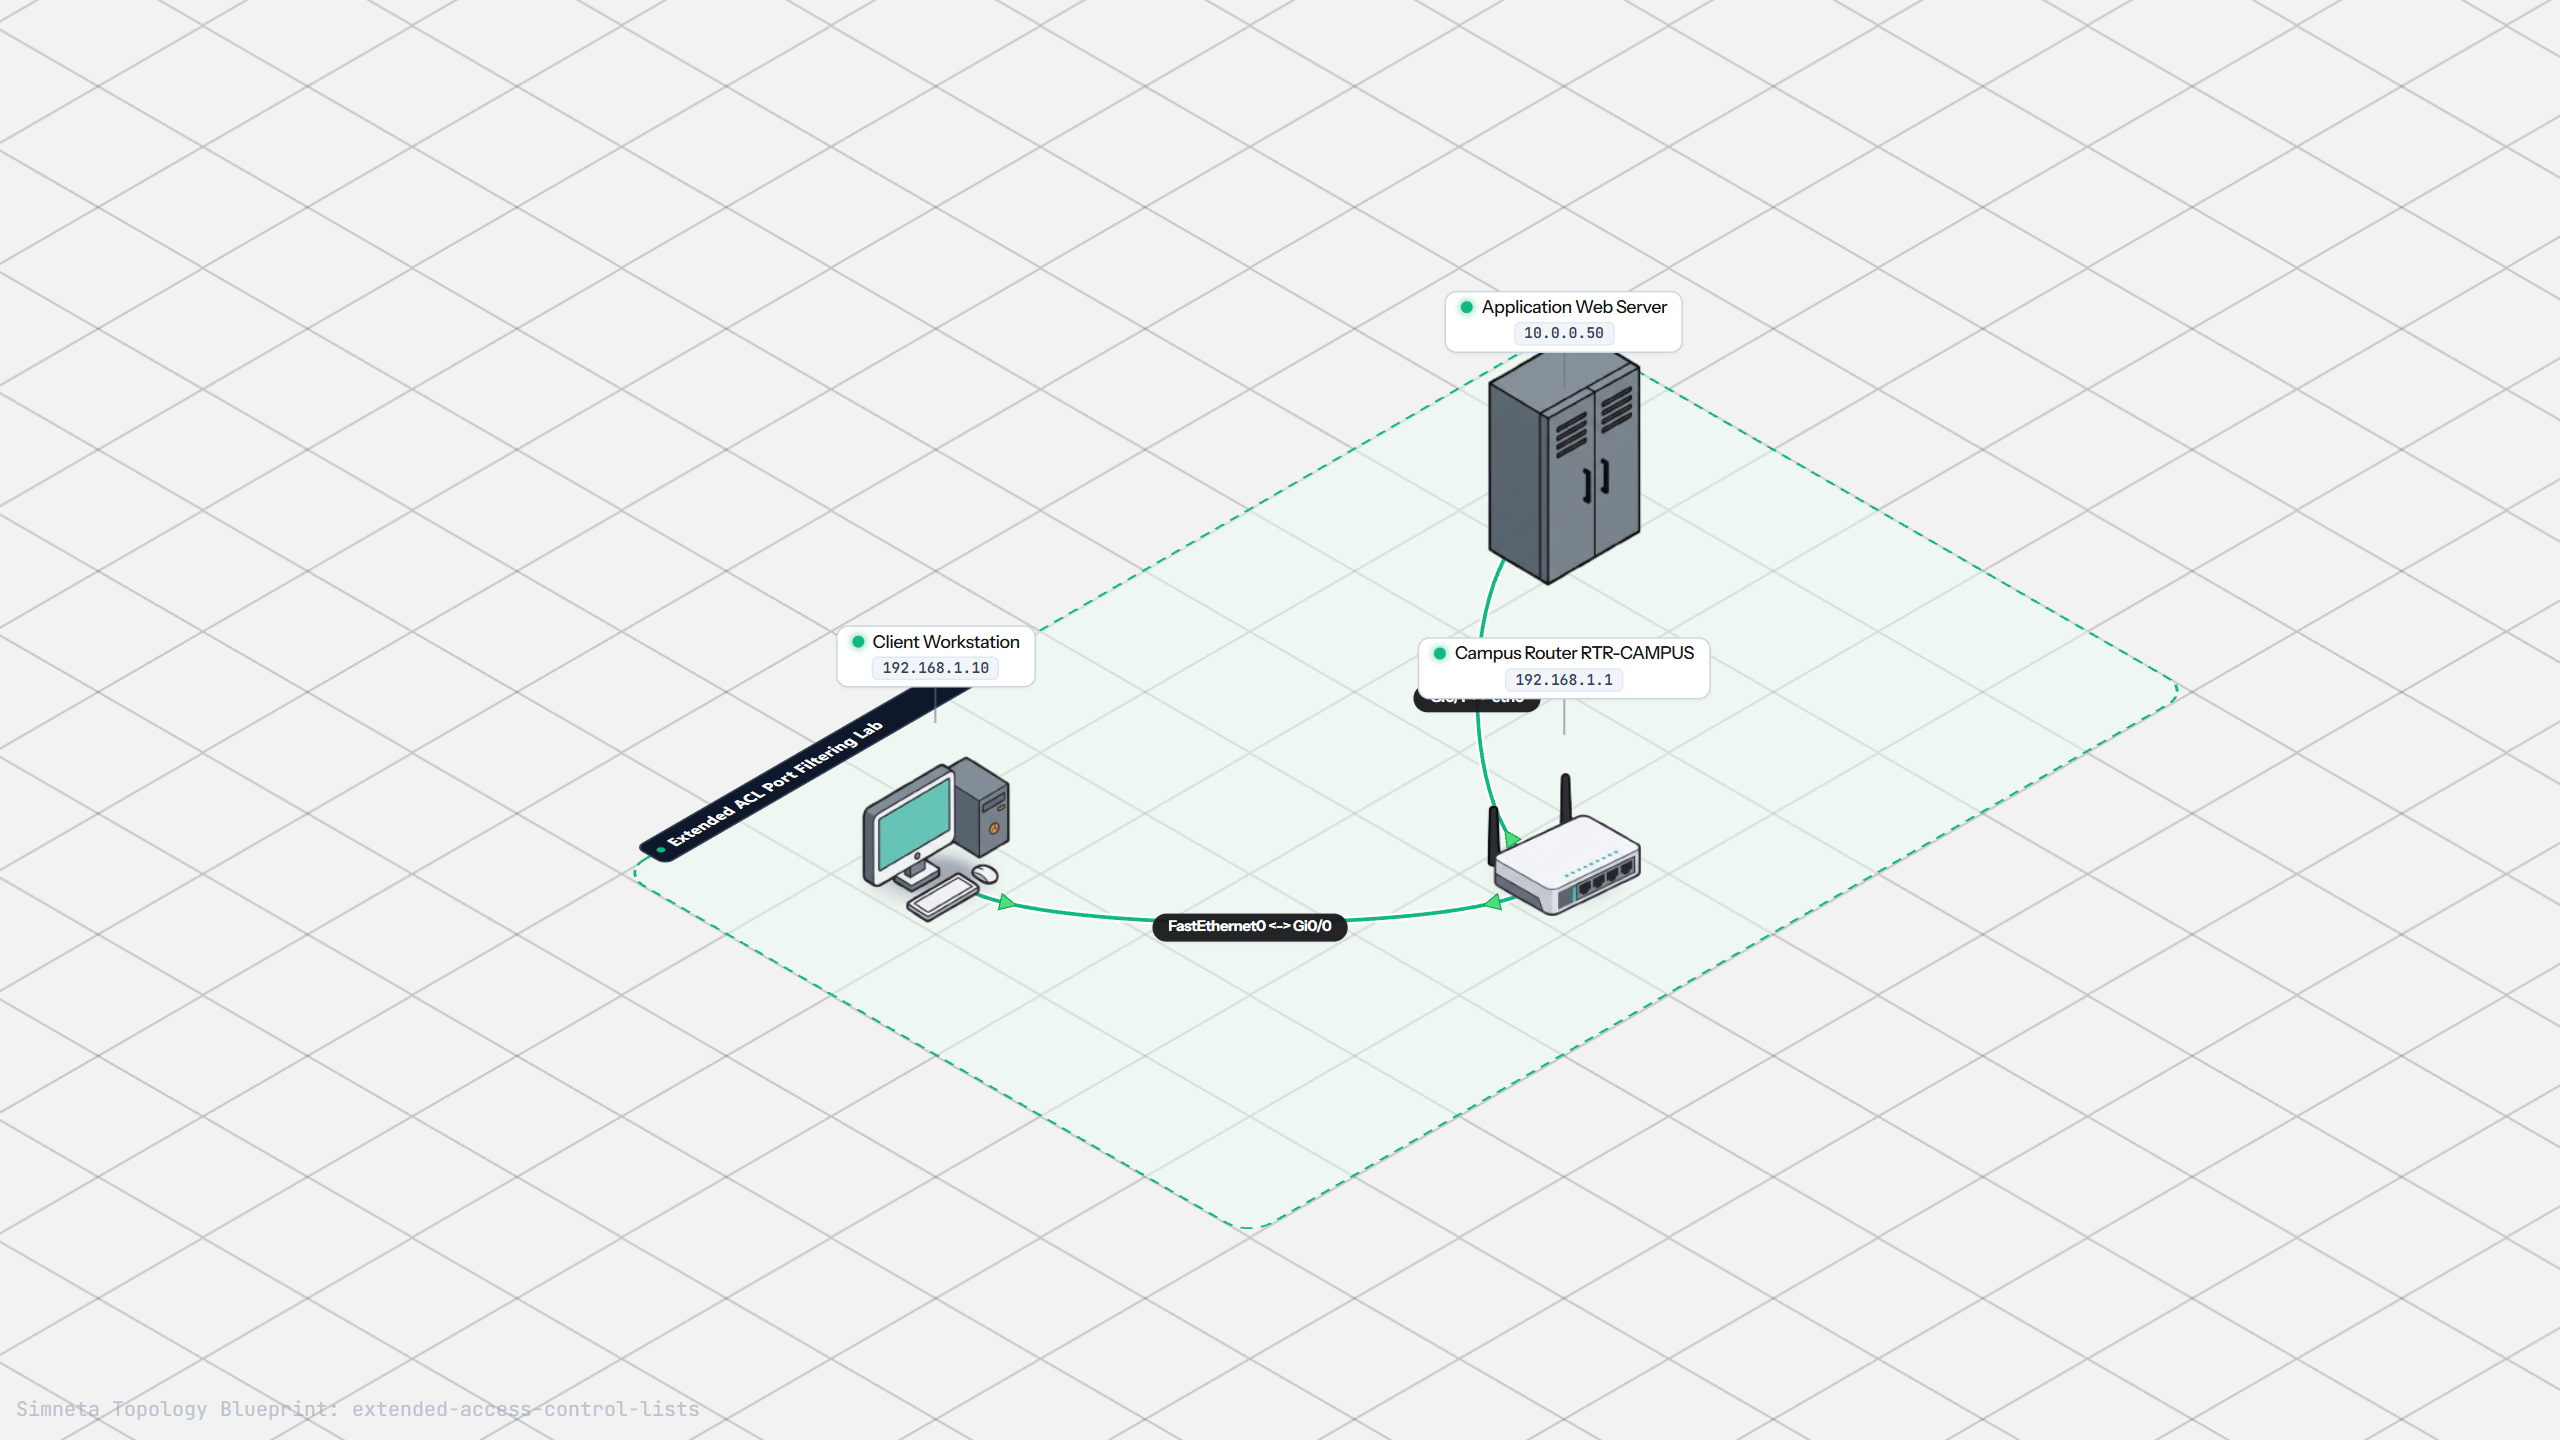
Harness the granular filtering precision of extended ACLs. Filter by source IP, destination IP, transport protocol, and TCP/UDP application port numbers.

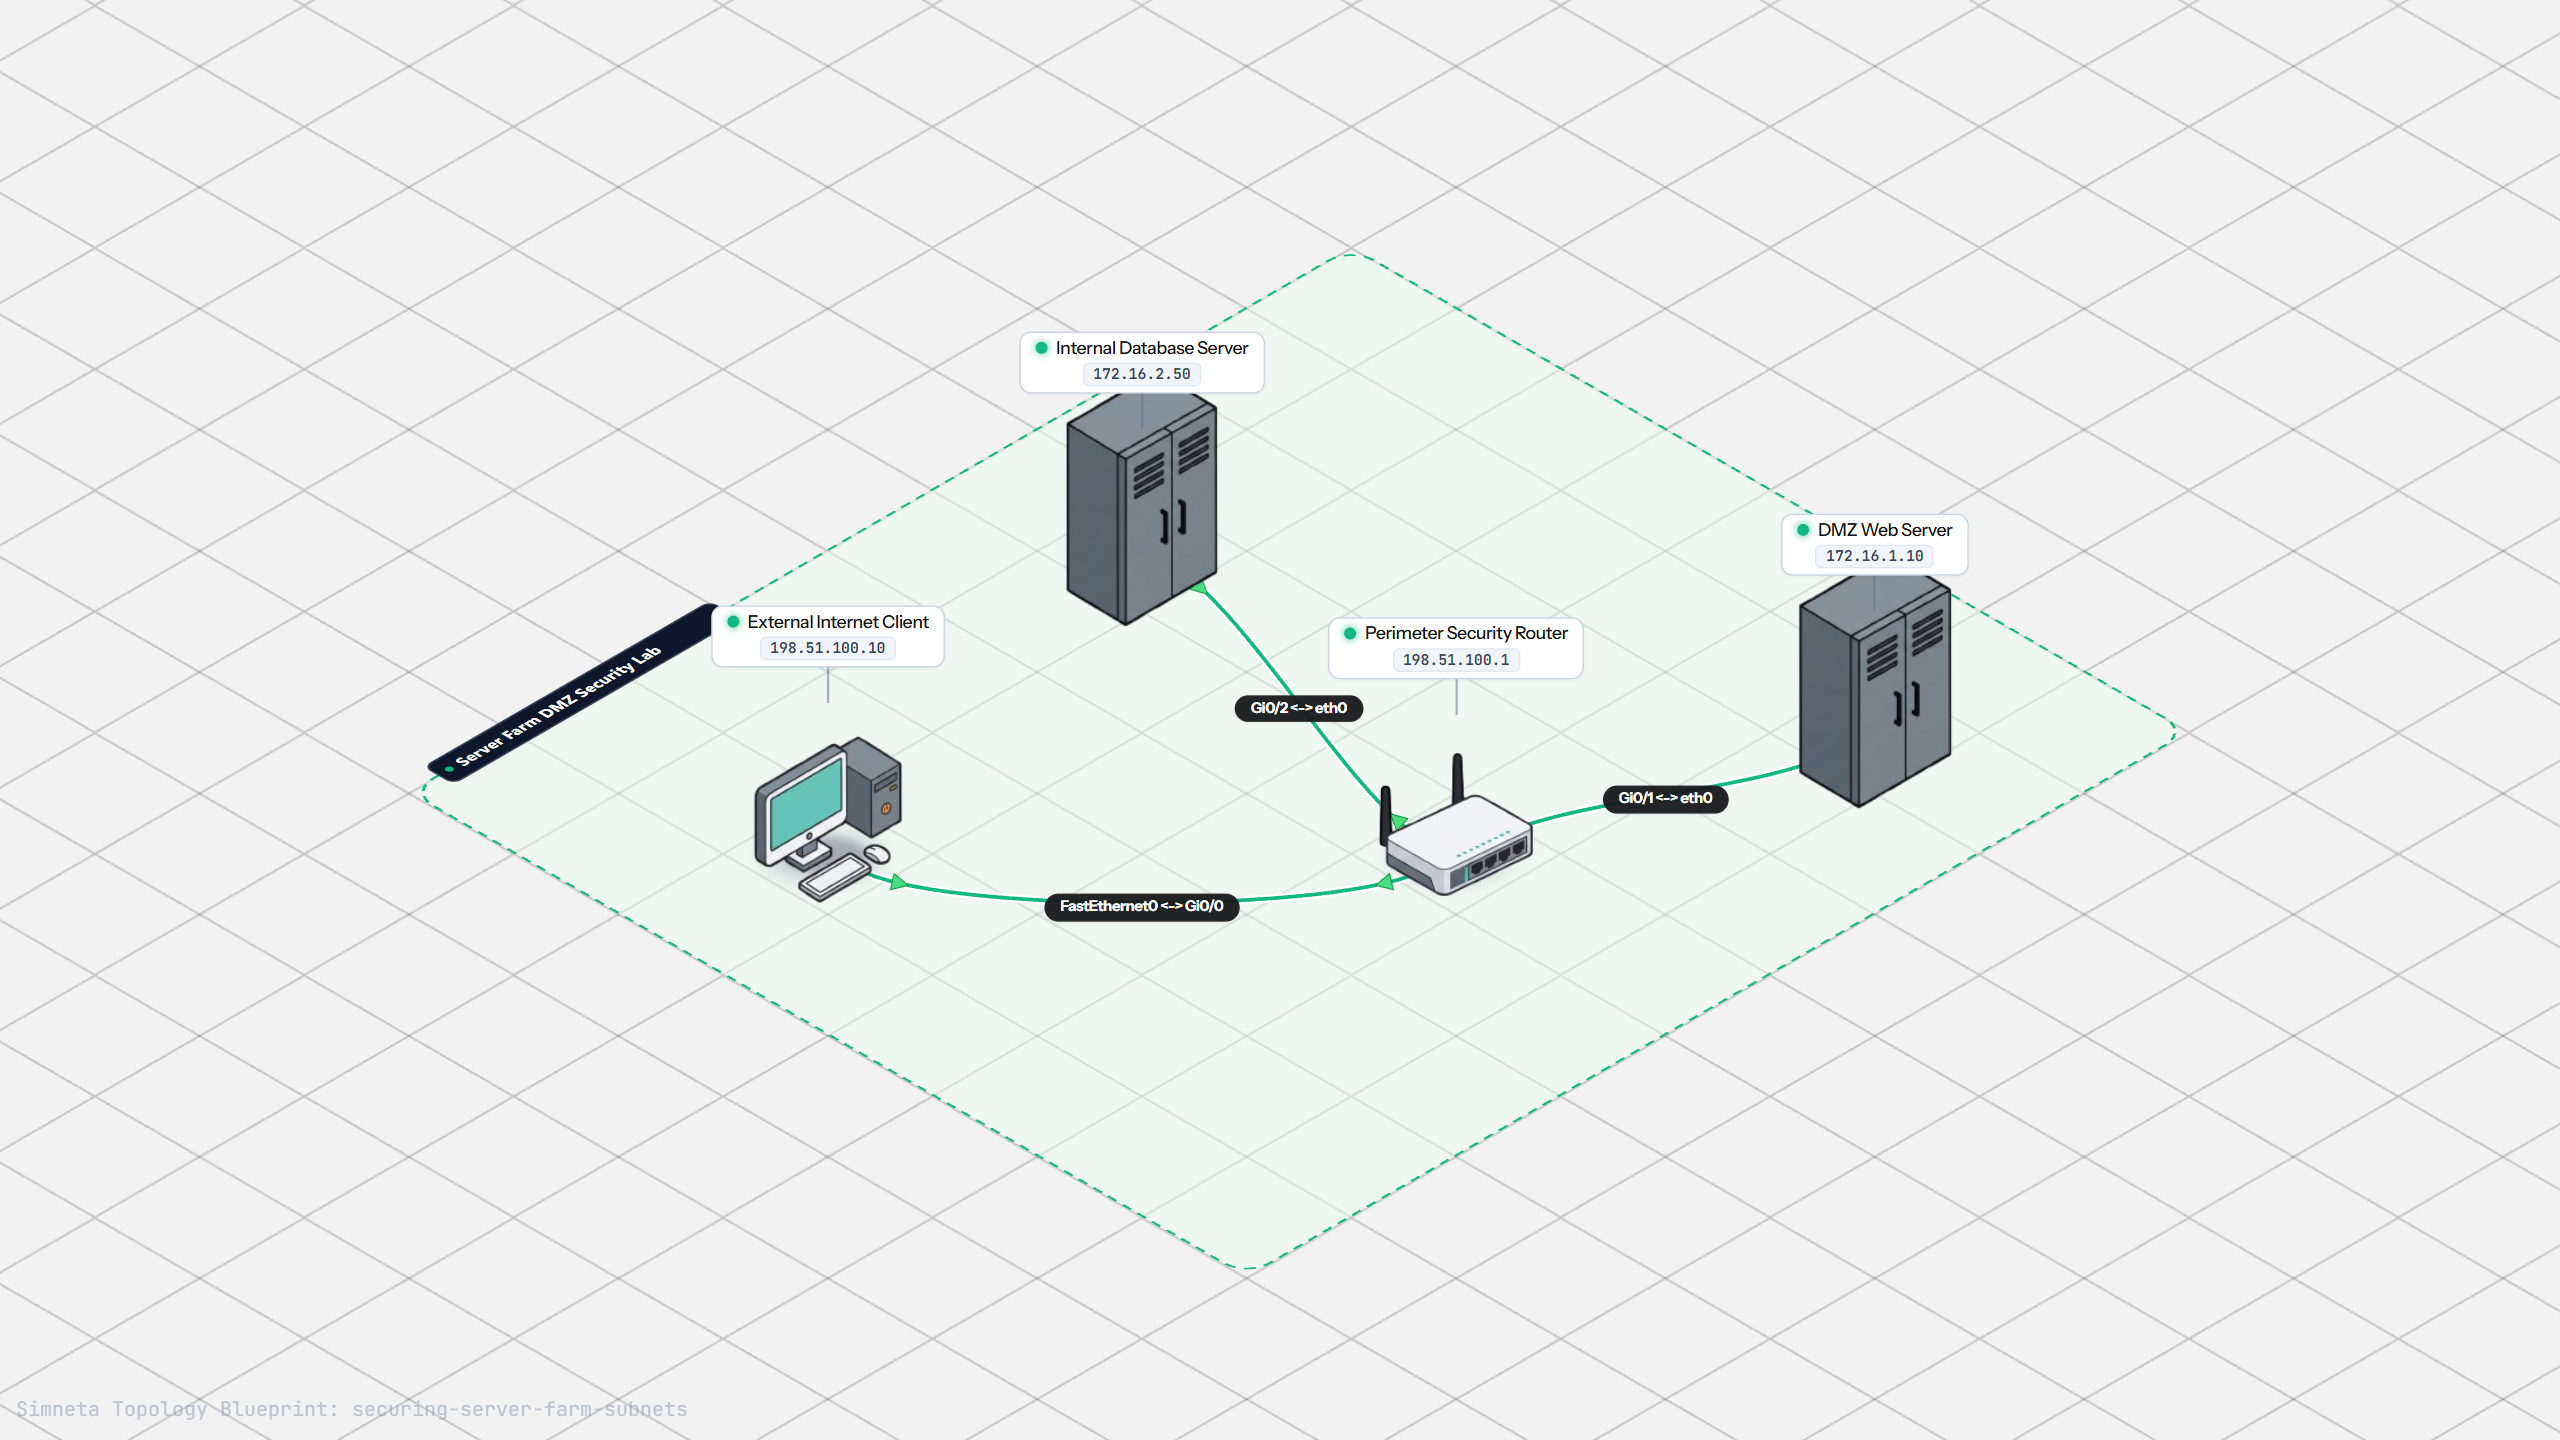
Design a multi-tier perimeter defense. Isolate public-facing DMZ web servers from internal database repositories using segmented access control policies.

Solidify your perimeter defense skills. Implement RFC 2827 / BCP 38 anti-spoofing ingress filters, block unauthorized WAN probes, and harden router control planes.